Deep Dive: Agent Identity and Trust Scores
· 12 min read
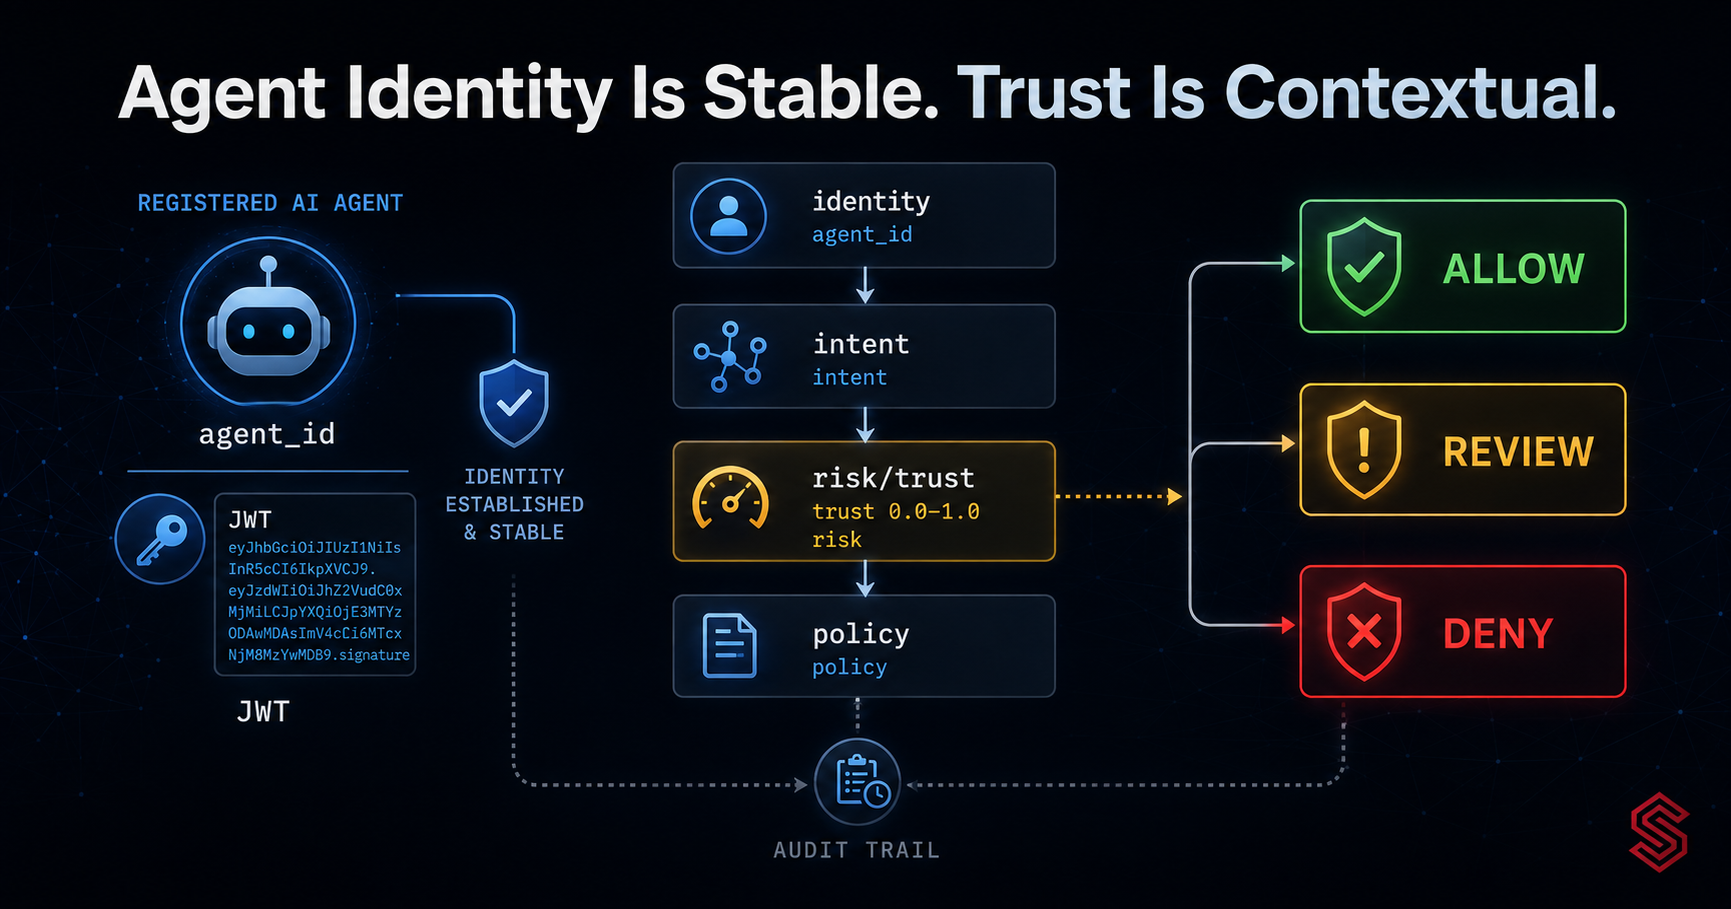
An AI agent presents a valid JWT and asks a billing API to issue a refund. The token is correctly signed, unexpired, and belongs to the expected agent. Is that enough to execute the request?
No—but not because authentication failed.
Authentication did its job: it established a verifiable identity for the caller. The remaining questions are different. Is the refund within the agent's assigned policy? Does the request express the intent the endpoint is meant to serve? Is the action unusually risky for this agent? Has the agent recently produced violations or required repeated human intervention? Should the request be allowed, denied, or held for review?