Zero Trust for AI Agents: Authentication Is Necessary, Not Sufficient
· 10 min read
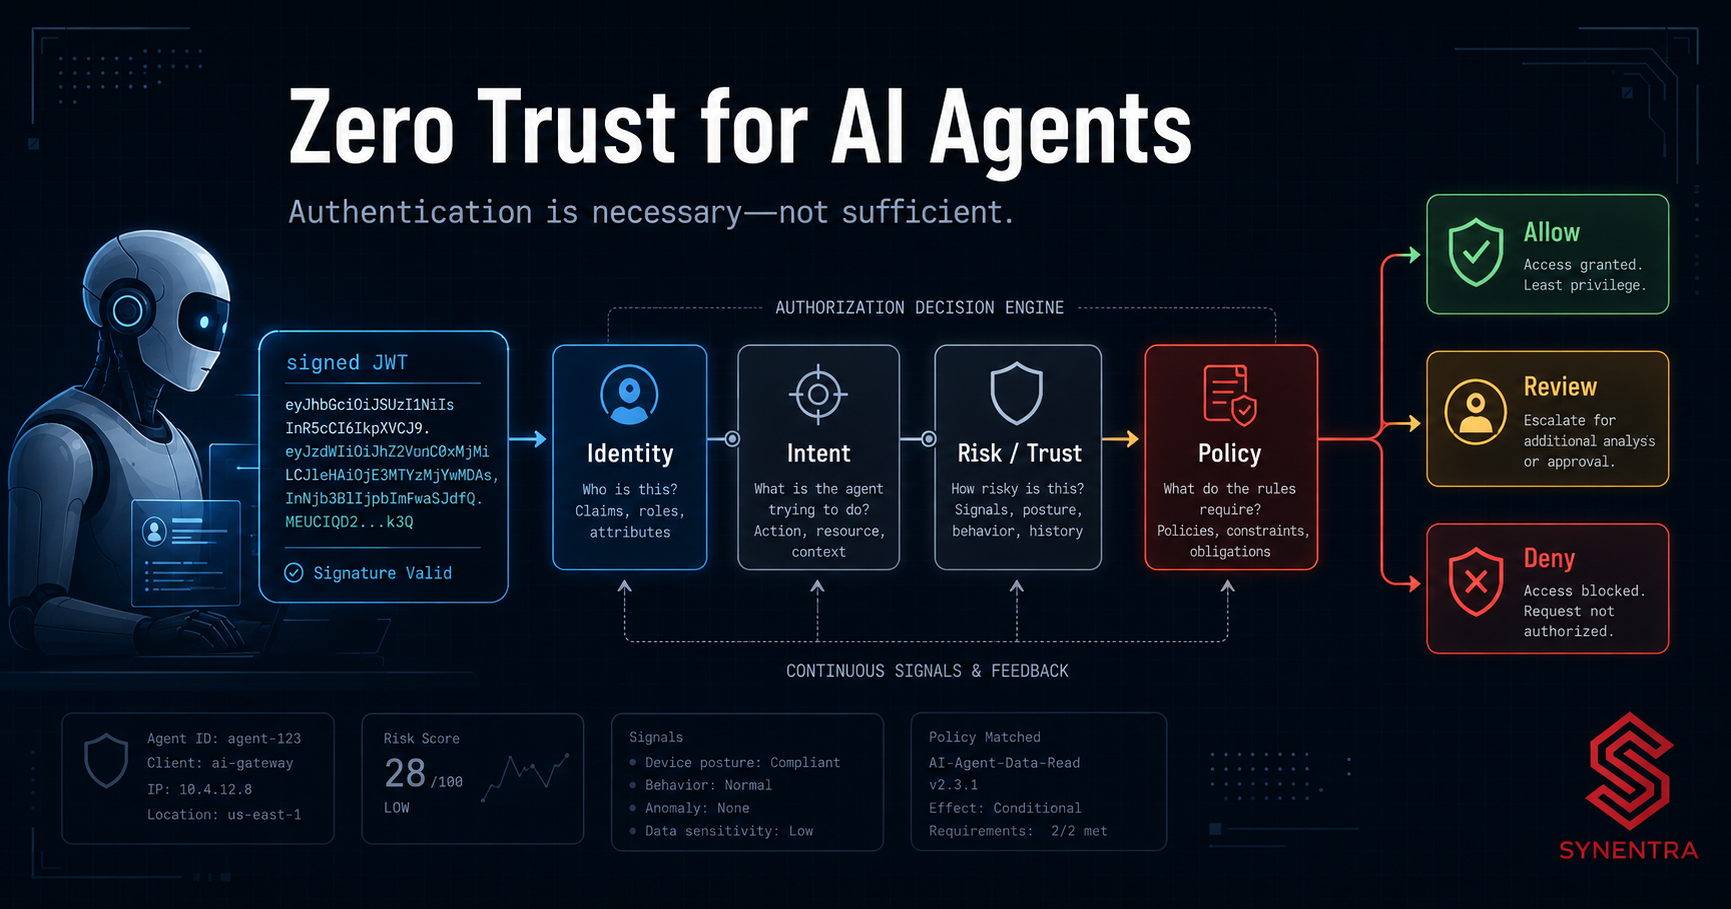
An AI agent presents a valid JWT. Its issuer is trusted, its signature is valid, its audience is correct, and its token has not expired.
The agent then asks a billing API to issue a high-value refund.
Should the request be allowed?
Authentication can establish which workload is making the request. It cannot, by itself, establish whether this action is appropriate now, for this resource, with this inferred purpose, under the current risk conditions. A token answers an identity question. Governance must answer a decision question.