Audit Logging: Compliance and Forensics
· 10 min read
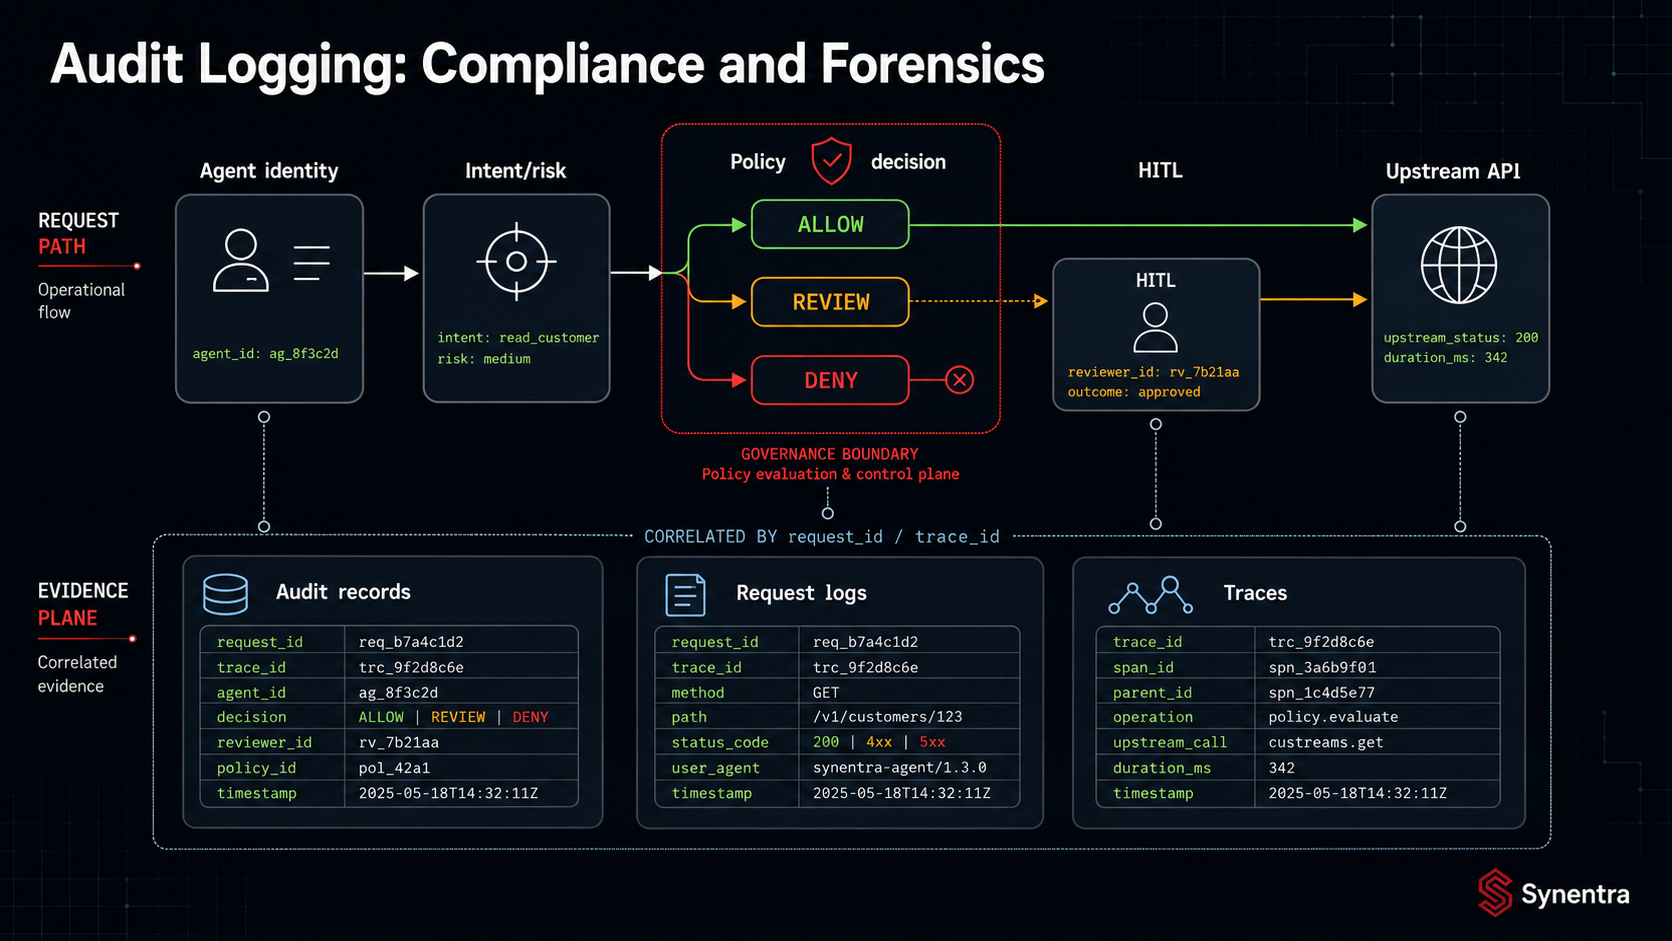
At 02:14 UTC, an autonomous agent sends DELETE /v1/customers/4821. The upstream API returns 204 No Content. At 09:00, an operator asks a simple question: why was that action allowed?
An access log can show that a request reached the service. An application log may show that a handler completed. A distributed trace can connect gateway and upstream spans. None of those records necessarily explains which agent acted, what intent was inferred, which policy result applied, what risk was calculated, whether human review occurred, or which final outcome the governance layer selected.